Your course library is a liability you can't see. Let's map it.
Large organizations don't lack training. They lack a way to know which courses still match their sources, and a safe way to update them. Coursecast's enterprise path starts with an audit and grows into governed, change-driven maintenance.
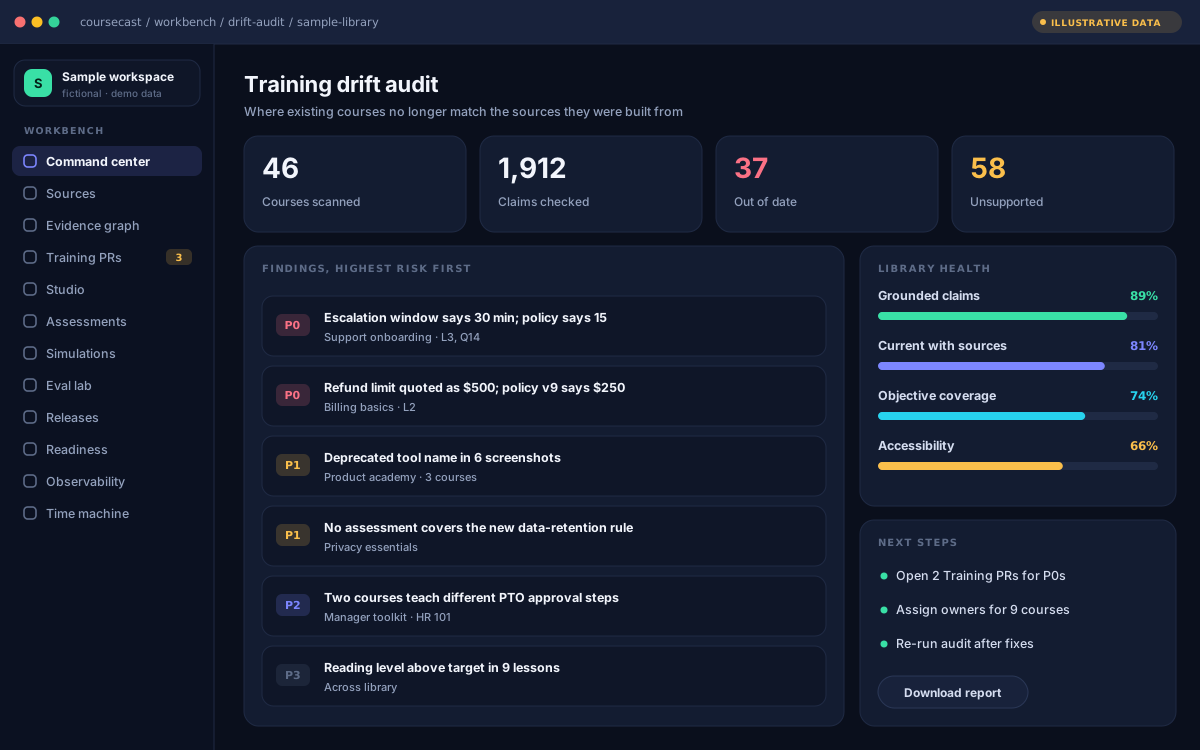
Three steps, each useful on its own
Training Drift Audit
We review one course library with you: inventory, sources, claim checks and a ranked findings report. Limited places for early design partners.
Draft & refresh
Use the live studio to redraft the highest-risk courses from current sources, with your SMEs reviewing.
Governed maintenance
Early access to the evidence graph, Training PRs and releases as they ship, shaped by your workflows.
Built for real organizational change
The enterprise layer we're designing with design partners. All roadmap.
Risk-based routing
Scrutiny proportional to the change.
Policy engine
Your rules applied to every release.
Owners everywhere
Every source and course has an accountable owner.
Historical proof
Reconstruct exactly what applied on any date.
Localization graph
Every locale linked to its source lesson.
Scheduled activation
Releases go live on the effective date.
Bulk migration
Bring the legacy estate in and find its drift.
Audit portal
Read-only evidence access for risk teams.
Identity & access
SSO and roles when accounts exist; not available today.
Questions your library should be able to answer
If any of these take more than a day to answer, you have a governance gap, not a content gap.
What we can tell your security team today
| Question | Coursecast today |
|---|---|
| Do you store uploaded documents? | No. Files are discarded when the drafting request finishes. |
| Where are drafts stored? | Only in the user's browser (local storage) until exported. |
| AI provider and training | Anthropic's Claude API. Commercial terms don't allow training on API inputs or outputs; Anthropic may keep API data for a limited period for safety and abuse monitoring. |
| Zero data retention? | Not claimed. |
| Certifications (SOC 2, ISO 27001) | None yet. We won't claim them until audited. |
| SSO / SAML / SCIM | Not available. No accounts exist in early access. |
| Transport | HTTPS only; HSTS; strict Content Security Policy; no third-party scripts. |
| Logs | Technical metadata only (time, hashed IP, file type and size, token counts); never document content. |
Tell us about your library
A person reads every message. We usually reply within one business day with next steps, or tell you honestly if we're not a fit yet.
- Roughly how many courses, and in which tools?
- Which sources change most often?
- Who reviews training today?